
MPLS VPN Hub and Spoke实验
实验拓扑
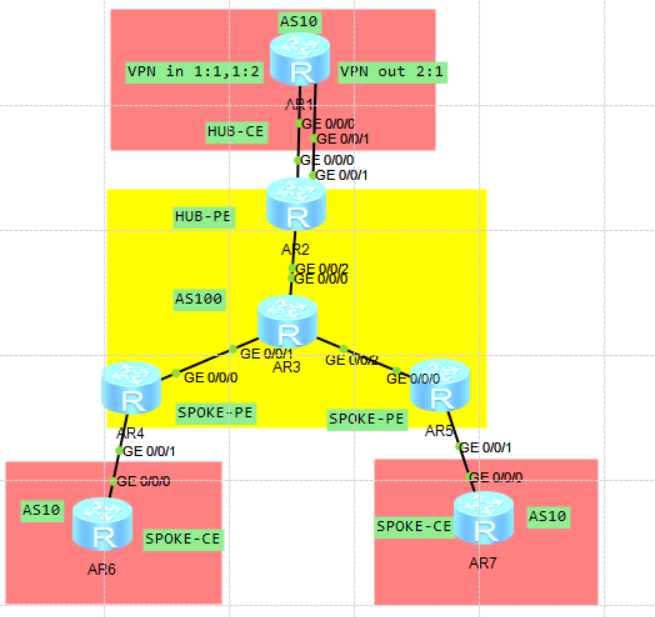

实验要求
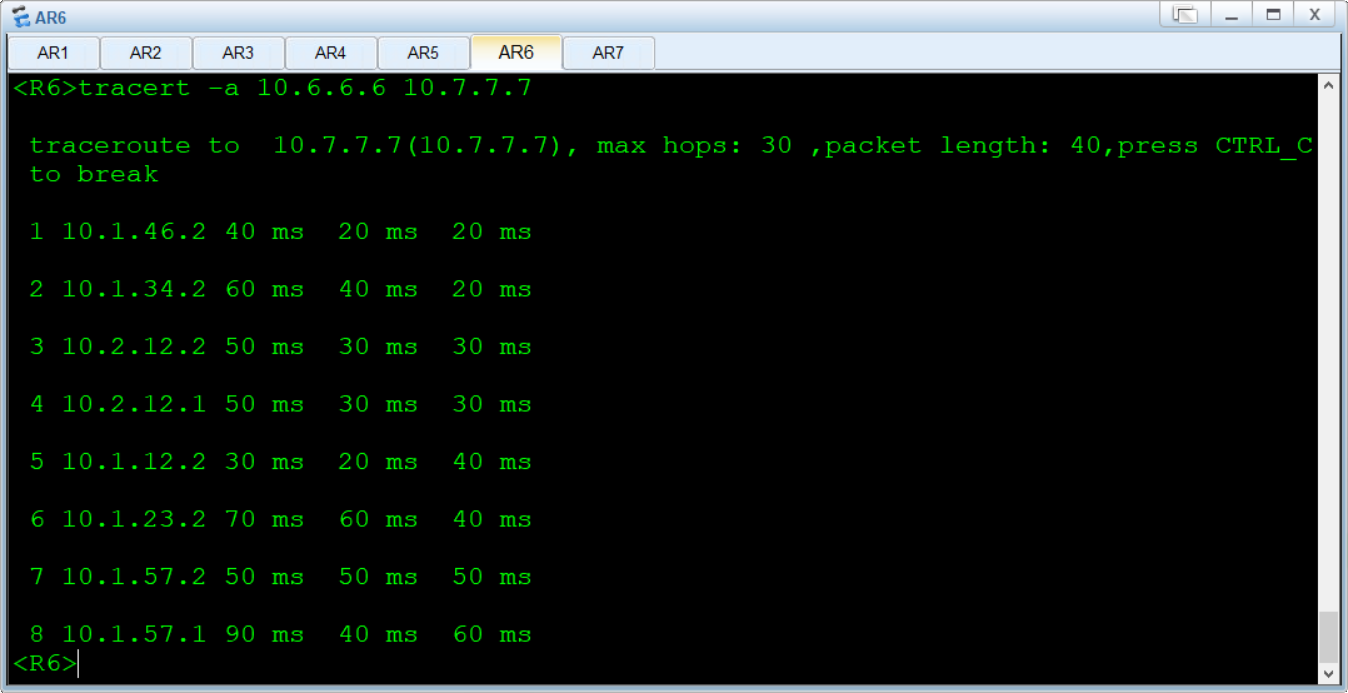
1.R6与R7通信需要经过R1,不可以直通
2.HUB-CE,SPOKE-CE在同一个AS(allow
-as-loop的合理使用)
3.各个PE与CE之间均为EBGP关系(也可以做IBGP,OSPF)
配置
1.R2,3,4,5配置路由,并启用ospf
2.PE之间配置MP-BGP邻居关系
(减少IBGP邻居的建立使用 RR 反射器,其中R2充当反射器最为合适)
3.R2,3,4,5启用MPLS
3.SPOKE-PE配置VPN实例,并进入接口进行绑定
4.HUB-PE上配置只进的VPN实例,和只出的VPN实例
5.配置PE与CE间路由交换(允许路由环路)
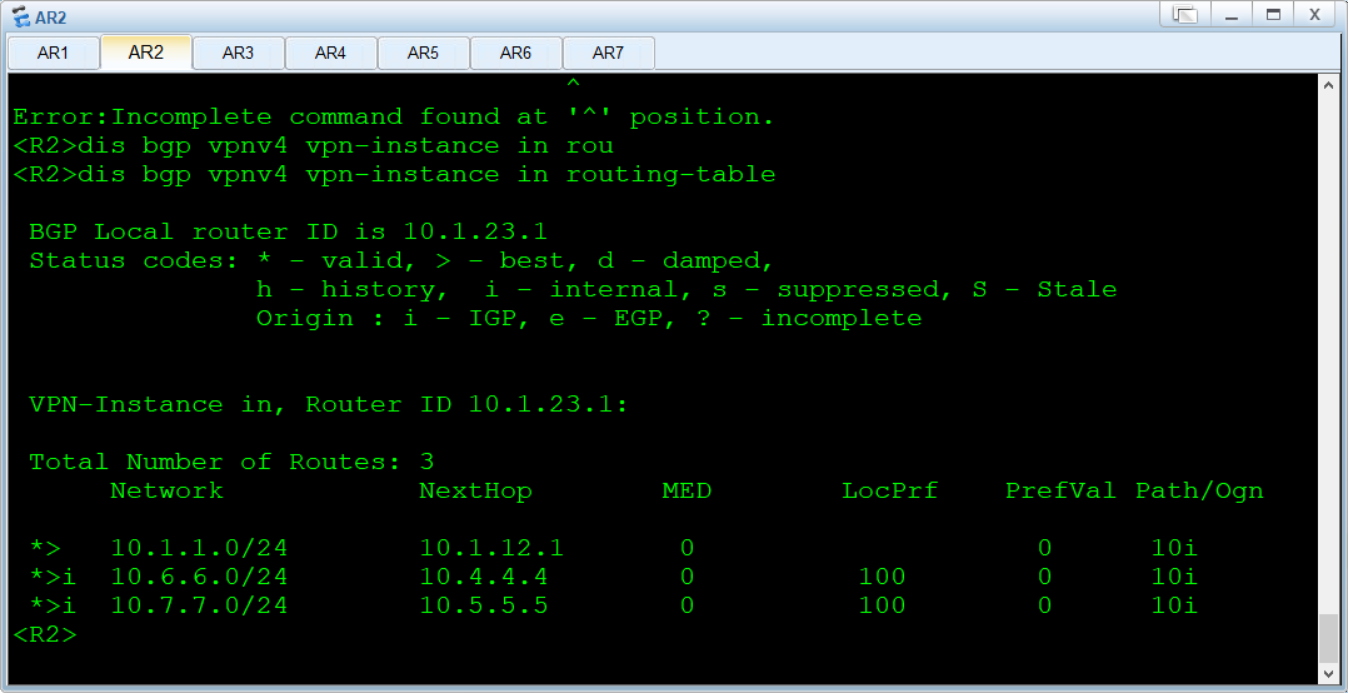
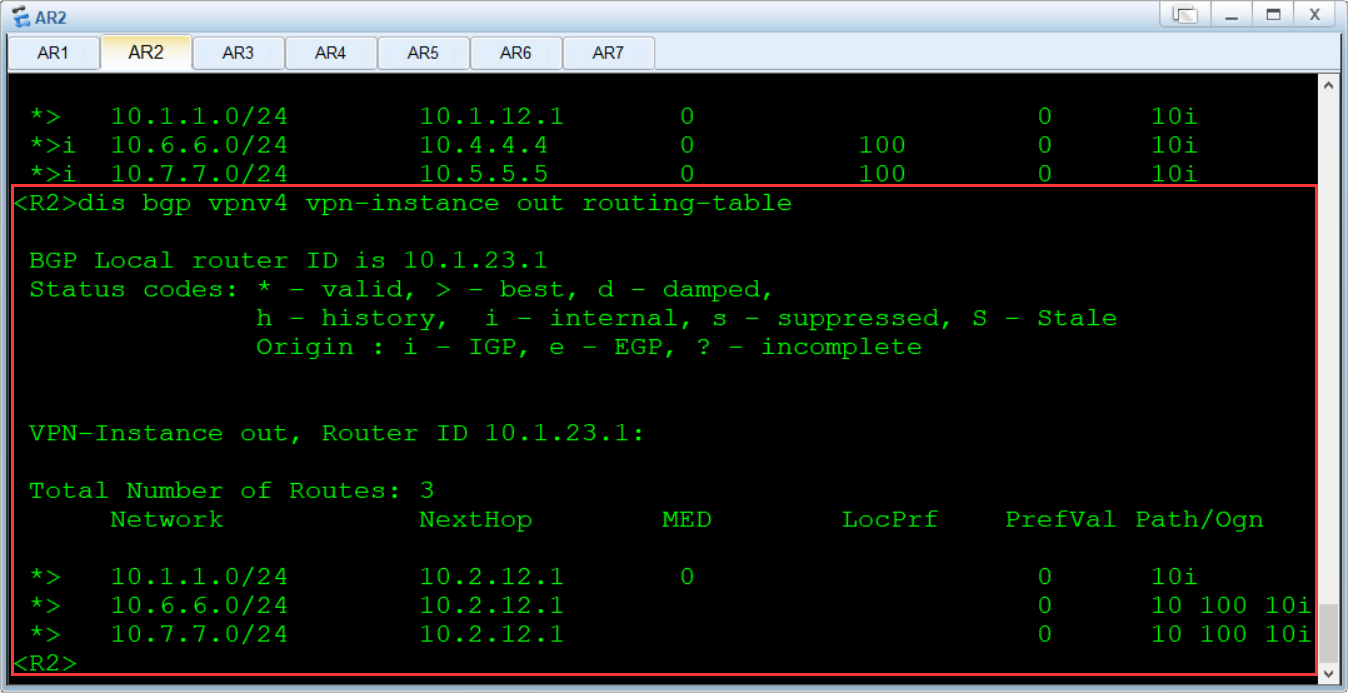
测试:
R2上dis bgp vpnv4 vpn-instance in routing-table
R2上dis bgp vpnv4 vpn-instance out routing-table
R6pingR7
全部配置:
R1
#
 sysname R1
#
interface GigabitEthernet0/0/0
 ip address 10.1.12.1 255.255.255.0
#
interface GigabitEthernet0/0/1
 ip address 10.2.12.1 255.255.255.0
#
interface GigabitEthernet0/0/2
#
interface NULL0
#
interface LoopBack0
 ip address 10.1.1.1 255.255.255.0
#
bgp 10
 peer 10.1.12.2 as-number 100
 peer 10.2.12.2 as-number 100
 #
 ipv4-family unicast
  undo synchronization
  network 10.1.1.0 255.255.255.0
  peer 10.1.12.2 enable
  peer 10.1.12.2 allow-as-loop
  peer 10.2.12.2 enable
  peer 10.2.12.2 allow-as-loop
#
R2
#
 sysname R2
#
ip vpn-instance in
 ipv4-family
  route-distinguisher 2:2
  vpn-target 1:1 1:2 import-extcommunity
#
ip vpn-instance out
 ipv4-family
  route-distinguisher 2:1
  vpn-target 2:1 export-extcommunity
#
mpls lsr-id 10.2.2.2
mpls
#
mpls ldp
#
interface GigabitEthernet0/0/0
 ip binding vpn-instance in
 ip address 10.1.12.2 255.255.255.0
#
interface GigabitEthernet0/0/1
 ip binding vpn-instance out
 ip address 10.2.12.2 255.255.255.0
#
interface GigabitEthernet0/0/2
 ip address 10.1.23.1 255.255.255.0
 mpls
 mpls ldp
#
interface NULL0
#
interface LoopBack0
 ip address 10.2.2.2 255.255.255.0
#
bgp 100
 peer 10.4.4.4 as-number 100
 peer 10.4.4.4 connect-interface LoopBack0
 peer 10.5.5.5 as-number 100
 peer 10.5.5.5 connect-interface LoopBack0
 #
 ipv4-family unicast
  undo synchronization
  peer 10.4.4.4 enable
  peer 10.4.4.4 reflect-client
  peer 10.4.4.4 next-hop-local
  peer 10.5.5.5 enable
  peer 10.5.5.5 reflect-client
  peer 10.5.5.5 next-hop-local
 #
 ipv4-family vpnv4
  policy vpn-target
  peer 10.4.4.4 enable
  peer 10.4.4.4 reflect-client
  peer 10.5.5.5 enable
  peer 10.5.5.5 reflect-client
 #
 ipv4-family vpn-instance in
  peer 10.1.12.1 as-number 10
 #
 ipv4-family vpn-instance out
  peer 10.2.12.1 as-number 10
  peer 10.2.12.1 allow-as-loop 2
#
ospf 1 router-id 2.2.2.2
 area 0.0.0.0
  network 10.1.23.0 0.0.0.255
  network 10.2.2.2 0.0.0.0
#
R3
#
 sysname R3
#
mpls lsr-id 10.3.3.3
mpls
#
mpls ldp
#
interface GigabitEthernet0/0/0
 ip address 10.1.23.2 255.255.255.0
 mpls
 mpls ldp
#
interface GigabitEthernet0/0/1
 ip address 10.1.34.2 255.255.255.0
 mpls
 mpls ldp
#
interface GigabitEthernet0/0/2
 ip address 10.1.35.2 255.255.255.0
 mpls
 mpls ldp
#
interface NULL0
#
interface LoopBack0
 ip address 10.3.3.3 255.255.255.0
#
ospf 1 router-id 3.3.3.3
 area 0.0.0.0
  network 10.1.23.0 0.0.0.255
  network 10.1.34.0 0.0.0.255
  network 10.1.35.0 0.0.0.255
  network 10.3.3.3 0.0.0.0
#
R4
#
 sysname R4
#
ip vpn-instance spoke
 ipv4-family
  route-distinguisher 1:1
  vpn-target 1:1 export-extcommunity
  vpn-target 2:1 import-extcommunity
#
mpls lsr-id 10.4.4.4
mpls
#
mpls ldp
#

interface GigabitEthernet0/0/0
 ip address 10.1.34.1 255.255.255.0
 mpls
 mpls ldp
#
interface GigabitEthernet0/0/1
 ip binding vpn-instance spoke
 ip address 10.1.46.2 255.255.255.0
#
interface GigabitEthernet0/0/2
#
interface NULL0
#
interface LoopBack0
 ip address 10.4.4.4 255.255.255.0
#
bgp 100
 peer 10.2.2.2 as-number 100
 peer 10.2.2.2 connect-interface LoopBack0
 #
 ipv4-family unicast
  undo synchronization
  peer 10.2.2.2 enable
  peer 10.2.2.2 next-hop-local
  peer 10.2.2.2 allow-as-loop
 #
 ipv4-family vpnv4
  policy vpn-target
  peer 10.2.2.2 enable
 #
 ipv4-family vpn-instance spoke
  peer 10.1.46.1 as-number 10
  peer 10.1.46.1 allow-as-loop
#
ospf 1 router-id 4.4.4.4
 area 0.0.0.0
  network 10.1.34.0 0.0.0.255
  network 10.4.4.4 0.0.0.0
#
R5
#
 sysname R5
#
ip vpn-instance spoke
 ipv4-family
  route-distinguisher 1:2
  vpn-target 1:2 export-extcommunity
  vpn-target 2:1 import-extcommunity
#
mpls lsr-id 10.5.5.5
mpls
#
mpls ldp
#
interface GigabitEthernet0/0/0
 ip address 10.1.35.1 255.255.255.0
 mpls
 mpls ldp
#
interface GigabitEthernet0/0/1
 ip binding vpn-instance spoke
 ip address 10.1.57.2 255.255.255.0
#
interface GigabitEthernet0/0/2
#
interface NULL0
#
interface LoopBack0
 ip address 10.5.5.5 255.255.255.0
#
bgp 100
 peer 10.2.2.2 as-number 100
 peer 10.2.2.2 connect-interface LoopBack0
 #
 ipv4-family unicast
  undo synchronization
  peer 10.2.2.2 enable
  peer 10.2.2.2 next-hop-local
  peer 10.2.2.2 allow-as-loop
 #
 ipv4-family vpnv4
  policy vpn-target
  peer 10.2.2.2 enable
 #
 ipv4-family vpn-instance spoke
  peer 10.1.57.1 as-number 10
  peer 10.1.57.1 allow-as-loop
#
ospf 1 router-id 5.5.5.5
 area 0.0.0.0
  network 10.1.35.0 0.0.0.255
  network 10.5.5.5 0.0.0.0
#
R6
#
 sysname R6
#
interface GigabitEthernet0/0/0
 ip address 10.1.46.1 255.255.255.0
#
interface GigabitEthernet0/0/1
#
interface GigabitEthernet0/0/2
#
interface NULL0
#
interface LoopBack0
 ip address 10.6.6.6 255.255.255.0
#
bgp 10
 peer 10.1.46.2 as-number 100
 #
 ipv4-family unicast
  undo synchronization
  network 10.6.6.0 255.255.255.0
  peer 10.1.46.2 enable
  peer 10.1.46.2 allow-as-loop 2
 #
 ipv4-family vpnv4
  policy vpn-target
#
R7
#
 sysname R7
#
interface GigabitEthernet0/0/0
 ip address 10.1.57.1 255.255.255.0
#
interface GigabitEthernet0/0/1
#
interface GigabitEthernet0/0/2
#
interface NULL0
#
interface LoopBack0
 ip address 10.7.7.7 255.255.255.0
#
bgp 10
 peer 10.1.57.2 as-number 100
 #
 ipv4-family unicast
  undo synchronization
  network 10.7.7.0 255.255.255.0
  peer 10.1.57.2 enable
  peer 10.1.57.2 allow-as-loop 2
#
版权声明:本文内容由互联网用户自发贡献,该文观点仅代表作者本人。本站仅提供信息存储空间服务,不拥有所有权,不承担相关法律责任。如发现本站有涉嫌侵权/违法违规的内容, 请发送邮件至 举报,一经查实,本站将立刻删除。
发布者:全栈程序员-站长,转载请注明出处:https://javaforall.net/100140.html原文链接:https://javaforall.net


