
Security problems is more and more important on the internet today. You can see the problems .
This chapter is really exciting, you can learn serveral ways of attacking the web application and the method to
protecting the websites. Somehow, you can be a hacker after studying.
1. Attack on the Admin page.
The last project, we can easy control to the admin user by accessing the admin page by URLs.
Thats the problem, if a hack can have the access to the admin user, it must be very bad.
Its also very simple to solve this problem. Using HTTP authentication to password protect the Admin page.
When a page is secured using HTTP authentication. a window pops up requesting the user name and password
before access is allowed to the protected page. we can limit access to the Admin page to a few peple as you
want.
you need to insert authorize.php script before you can visit the admin page.
/*** authorize.php ***/



<?php
  // User name and password for authentication
  $username = 'rock';
  $password = 'roll';

  if (!isset($_SERVER['PHP_AUTH_USER']) || !isset($_SERVER['PHP_AUTH_PW']) ||
    ($_SERVER['PHP_AUTH_USER'] != $username) || ($_SERVER['PHP_AUTH_PW'] != $password)) {
    // The user name/password are incorrect so send the authentication headers
    header('HTTP/1.1 401 Unauthorized');
    header('WWW-Authenticate: Basic realm="Guitar Wars"');
    exit('<h2>Guitar Wars</h2>Sorry, you must enter a valid user name and password to access this page.');
  }
?>
View Code
2. The URL attacks
If the hacker has remembered the URLS of the removescore.php , he doesnt need to visit this page through
the admin Page, he can visit it directly by the URLs. so to avoid this happening, you just need to add the
authorize.php script to every page you want to protect. Just a little change can be done.
<?php
  require_once('authorize.php');
?>
add the codes at the front of each page you want to protect .
3. Attack on the high socres clones
this requires the humans to get all the datas available. we need to change the database and add some authorize
to the adminstrator. so he can decides if the data is valuable or not.
4. SQL injection.
This is really cool tech in hacks. You can even attack some websites that didnt have a protection. Lets see how
to do the SQL injection. I think this is really interesting. So I trace the code by PHP debug, you can see more clearly :
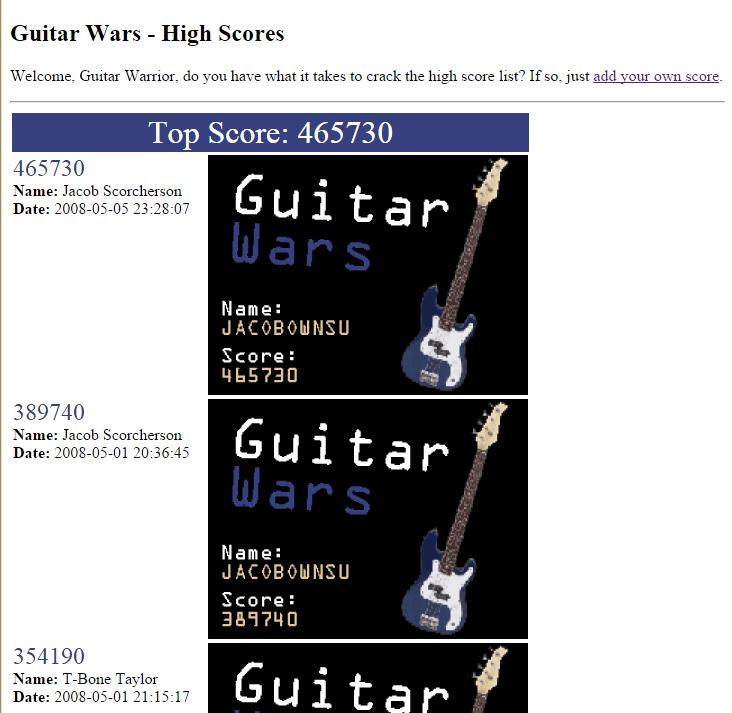
1) at first, the index page looks just right :
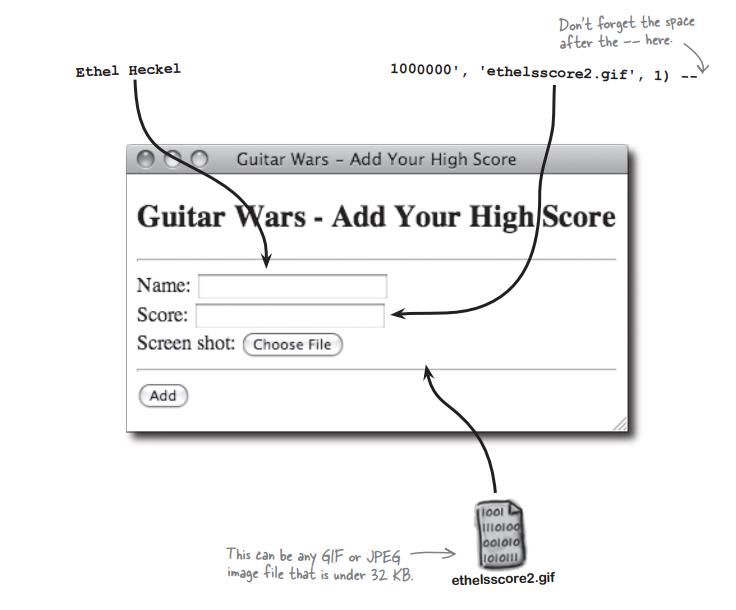
2) you can click the link to add your score :
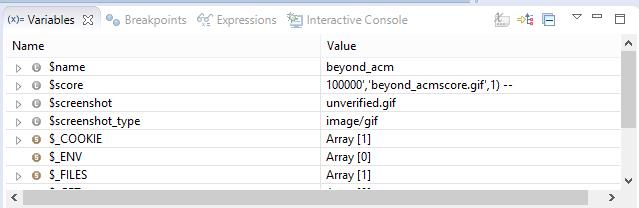
3) we use the PHP debug to see what is going on here : what was posted to the server just as follows :
4) the query just looks like this :
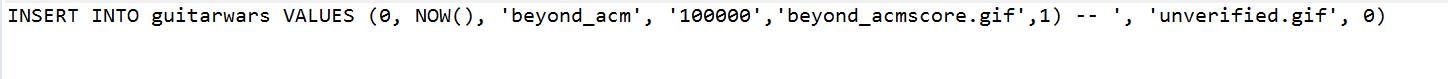
5) then quering this query , and bad things just happened :
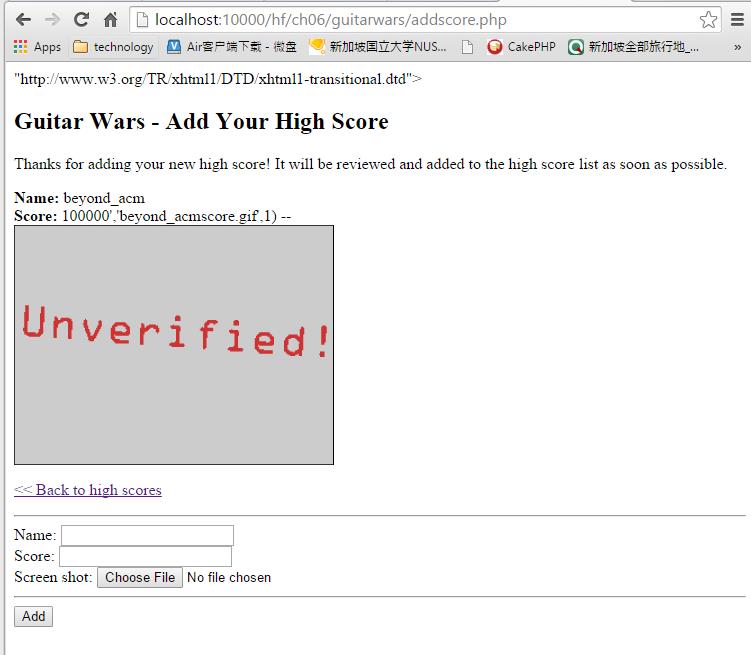
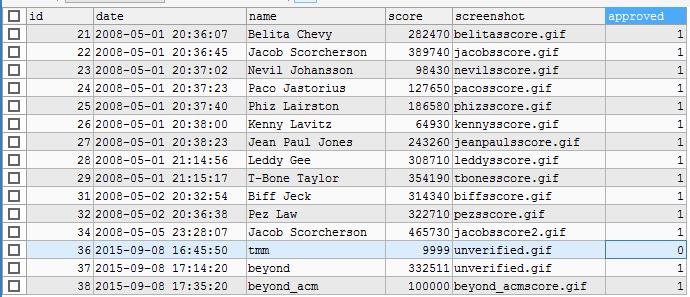
check the database , you will see the record was insert into the database susccess.
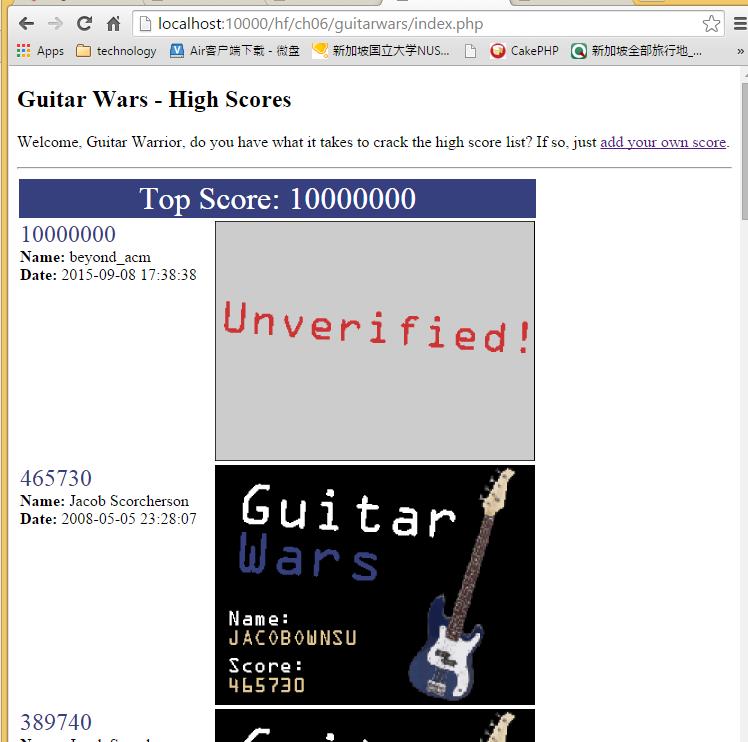
6) lets go back to the index.php, you will see the bad results : this is what SQL injection doing :
It is also quite easy to avoid the SQL Injection using PHP, you can use the trim() function
to gets rid of leading and trailing spaces in the form data.
just ran all form data through the trim() function before using it in an SQL query.
And you also need another built-in function, mysqli_real_escape_string()
this function converts dangerous characters into an escaped format that wont adversely affect SQL queries.
the project files as follows :
/*** index.php ***/
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN"
  "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd">
<html xmlns="http://www.w3.org/1999/xhtml" xml:lang="en" lang="en">
<head>
  <meta http-equiv="Content-Type" content="text/html; charset=utf-8" />
  <title>Guitar Wars - High Scores</title>
  <link rel="stylesheet" type="text/css" href="style.css" />
</head>
<body>
  <h2>Guitar Wars - High Scores</h2>
  <p>Welcome, Guitar Warrior, do you have what it takes to crack the high score list? If so, just <a href="addscore.php">add your own score</a>.</p>
  <hr />

<?php
  require_once('appvars.php');
  require_once('connectvars.php');

  // Connect to the database
  $dbc = mysqli_connect(DB_HOST, DB_USER, DB_PASSWORD, DB_NAME);

  // Retrieve the score data from MySQL
  $query = "SELECT * FROM guitarwars WHERE approved=1 ORDER BY score DESC, DATE ASC";
  $data = mysqli_query($dbc, $query);

  // Loop through the array of score data, formatting it as HTML
  echo '<table>';
  $i = 0;
  while ($row = mysqli_fetch_array($data)) {
    // Display the score data
    if ($i == 0) {
      echo '<tr><td colspan="2" class="topscoreheader">Top Score: ' . $row['score'] . '</td></tr>';
    }
    echo '<tr><td class="scoreinfo">';
    echo '<span class="score">' . $row['score'] . '</span><br />';
    echo '<strong>Name:</strong> ' . $row['name'] . '<br />';
    echo '<strong>Date:</strong> ' . $row['date'] . '</td>';
    if (is_file(GW_UPLOADPATH . $row['screenshot']) && filesize(GW_UPLOADPATH . $row['screenshot']) > 0) {
      echo '<td><img src="' . GW_UPLOADPATH . $row['screenshot'] . '" alt="Score image" /></td></tr>';
    }
    else {
      echo '<td><img src="' . GW_UPLOADPATH . 'unverified.gif' . '" alt="Unverified score" /></td></tr>';
    }
    $i++;
  }
  echo '</table>';

  mysqli_close($dbc);
?>

</body>
</html>
View Code
/*** addscore.php ***/
<!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd"> <html xmlns="http://www.w3.org/1999/xhtml" xml:lang="en" lang="en"> <head> <meta http-equiv="Content-Type" content="text/html; charset=utf-8" /> <title>Guitar Wars - Add Your High Score</title> <link rel="stylesheet" type="text/css" href="style.css" /> </head> <body> <h2>Guitar Wars - Add Your High Score</h2> <?php require_once('appvars.php'); require_once('connectvars.php'); if (isset($_POST['submit'])) { // Connect to the database $dbc = mysqli_connect(DB_HOST, DB_USER, DB_PASSWORD, DB_NAME); // Grab the score data from the POST $name = mysqli_real_escape_string($dbc, trim($_POST['name'])); $score = mysqli_real_escape_string($dbc, trim($_POST['score'])); $screenshot = mysqli_real_escape_string($dbc, trim($_FILES['screenshot']['name'])); $screenshot_type = $_FILES['screenshot']['type']; $screenshot_size = $_FILES['screenshot']['size']; if (!empty($name) && is_numeric($score) && !empty($screenshot)) { if ((($screenshot_type == 'image/gif') || ($screenshot_type == 'image/jpeg') || ($screenshot_type == 'image/pjpeg') || ($screenshot_type == 'image/png')) && ($screenshot_size > 0) && ($screenshot_size <= GW_MAXFILESIZE)) { if ($_FILES['screenshot']['error'] == 0) { // Move the file to the target upload folder $target = GW_UPLOADPATH . $screenshot; if (move_uploaded_file($_FILES['screenshot']['tmp_name'], $target)) { // Write the data to the database $query = "INSERT INTO guitarwars (date, name, score, screenshot) VALUES (NOW(), '$name', '$score', '$screenshot')"; mysqli_query($dbc, $query); // Confirm success with the user echo '<p>Thanks for adding your new high score! It will be reviewed and added to the high score list as soon as possible.</p>'; echo '<p><strong>Name:</strong> ' . $name . '<br />'; echo '<strong>Score:</strong> ' . $score . '<br />'; echo '<img src="' . GW_UPLOADPATH . $screenshot . '" alt="Score image" /></p>'; echo '<p><a href="index.php"><< Back to high scores</a></p>'; // Clear the score data to clear the form $name = ""; $score = ""; $screenshot = ""; mysqli_close($dbc); } else { echo '<p class="error">Sorry, there was a problem uploading your screen shot image.</p>'; } } } else { echo '<p class="error">The screen shot must be a GIF, JPEG, or PNG image file no greater than ' . (GW_MAXFILESIZE / 1024) . ' KB in size.</p>'; } // Try to delete the temporary screen shot image file @unlink($_FILES['screenshot']['tmp_name']); } else { echo '<p class="error">Please enter all of the information to add your high score.</p>'; } } ?> <hr /> <form enctype="multipart/form-data" method="post" action="<?php echo $_SERVER['PHP_SELF']; ?>"> <input type="hidden" name="MAX_FILE_SIZE" value="<?php echo GW_MAXFILESIZE; ?>" /> <label for="name">Name:</label> <input type="text" id="name" name="name" value="<?php if (!empty($name)) echo $name; ?>" /><br /> <label for="score">Score:</label> <input type="text" id="score" name="score" value="<?php if (!empty($score)) echo $score; ?>" /><br /> <label for="screenshot">Screen shot:</label> <input type="file" id="screenshot" name="screenshot" /> <hr /> <input type="submit" value="Add" name="submit" /> </form> </body> </html>
View Code
/*** authorize.php ***/
<?php
  // User name and password for authentication
  $username = 'rock';
  $password = 'roll';

  if (!isset($_SERVER['PHP_AUTH_USER']) || !isset($_SERVER['PHP_AUTH_PW']) ||
    ($_SERVER['PHP_AUTH_USER'] != $username) || ($_SERVER['PHP_AUTH_PW'] != $password)) {
    // The user name/password are incorrect so send the authentication headers
    header('HTTP/1.1 401 Unauthorized');
    header('WWW-Authenticate: Basic realm="Guitar Wars"');
    exit('<h2>Guitar Wars</h2>Sorry, you must enter a valid user name and password to access this page.');
  }
?>
View Code
/*** approvescore.php ***/
<?php require_once('authorize.php'); ?> <!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd"> <html xmlns="http://www.w3.org/1999/xhtml" xml:lang="en" lang="en"> <head> <meta http-equiv="Content-Type" content="text/html; charset=utf-8" /> <title>Guitar Wars - Approve a High Score</title> <link rel="stylesheet" type="text/css" href="style.css" /> </head> <body> <h2>Guitar Wars - Approve a High Score</h2> <?php require_once('appvars.php'); require_once('connectvars.php'); if (isset($_GET['id']) && isset($_GET['date']) && isset($_GET['name']) && isset($_GET['score'])) { // Grab the score data from the GET $id = $_GET['id']; $date = $_GET['date']; $name = $_GET['name']; $score = $_GET['score']; $screenshot = $_GET['screenshot']; } else if (isset($_POST['id']) && isset($_POST['name']) && isset($_POST['score'])) { // Grab the score data from the POST $id = $_POST['id']; $name = $_POST['name']; $score = $_POST['score']; } else { echo '<p class="error">Sorry, no high score was specified for approval.</p>'; } if (isset($_POST['submit'])) { if ($_POST['confirm'] == 'Yes') { // Connect to the database $dbc = mysqli_connect(DB_HOST, DB_USER, DB_PASSWORD, DB_NAME); // Approve the score by setting the approved column in the database $query = "UPDATE guitarwars SET approved = 1 WHERE id = $id"; mysqli_query($dbc, $query); mysqli_close($dbc); // Confirm success with the user echo '<p>The high score of ' . $score . ' for ' . $name . ' was successfully approved.'; } else { echo '<p class="error">Sorry, there was a problem approving the high score.</p>'; } } else if (isset($id) && isset($name) && isset($date) && isset($score)) { echo '<p>Are you sure you want to approve the following high score?</p>'; echo '<p><strong>Name: </strong>' . $name . '<br /><strong>Date: </strong>' . $date . '<br /><strong>Score: </strong>' . $score . '</p>'; echo '<form method="post" action="approvescore.php">'; echo '<img src="' . GW_UPLOADPATH . $screenshot . '" width="160" alt="Score image" /><br />'; echo '<input type="radio" name="confirm" value="Yes" /> Yes '; echo '<input type="radio" name="confirm" value="No" checked="checked" /> No <br />'; echo '<input type="submit" value="Submit" name="submit" />'; echo '<input type="hidden" name="id" value="' . $id . '" />'; echo '<input type="hidden" name="name" value="' . $name . '" />'; echo '<input type="hidden" name="score" value="' . $score . '" />'; echo '</form>'; } echo '<p><a href="admin.php"><< Back to admin page</a></p>'; ?> </body> </html>
View Code
/*** appvars.php ***/
<?php
  // Define application constants
  define('GW_UPLOADPATH', 'images/');
  define('GW_MAXFILESIZE', 32768);      // 32 KB
?>
View Code
/*** connectvars.php ***/
<?php
  // Define database connection constants
  define('DB_HOST', 'localhost');
  define('DB_USER', 'root');
  define('DB_PASSWORD', 'root');
  define('DB_NAME', 'gwdb');
?>
View Code
/*** admin.php ***/
<?php require_once('authorize.php'); ?> <!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd"> <html xmlns="http://www.w3.org/1999/xhtml" xml:lang="en" lang="en"> <head> <meta http-equiv="Content-Type" content="text/html; charset=utf-8" /> <title>Guitar Wars - High Scores Administration</title> <link rel="stylesheet" type="text/css" href="style.css" /> </head> <body> <h2>Guitar Wars - High Scores Administration</h2> <p>Below is a list of all Guitar Wars high scores. Use this page to remove scores as needed.</p> <hr /> <?php require_once('appvars.php'); require_once('connectvars.php'); // Connect to the database $dbc = mysqli_connect(DB_HOST, DB_USER, DB_PASSWORD, DB_NAME); // Retrieve the score data from MySQL $query = "SELECT * FROM guitarwars ORDER BY score DESC, date ASC"; $data = mysqli_query($dbc, $query); // Loop through the array of score data, formatting it as HTML echo '<table>'; echo '<tr><th>Name</th><th>Date</th><th>Score</th><th>Action</th></tr>'; while ($row = mysqli_fetch_array($data)) { // Display the score data echo '<tr class="scorerow"><td><strong>' . $row['name'] . '</strong></td>'; echo '<td>' . $row['date'] . '</td>'; echo '<td>' . $row['score'] . '</td>'; echo '<td><a href="removescore.php?id=' . $row['id'] . '&date=' . $row['date'] . '&name=' . $row['name'] . '&score=' . $row['score'] . '&screenshot=' . $row['screenshot'] . '">Remove</a>'; if ($row['approved'] == '0') { echo ' / <a href="approvescore.php?id=' . $row['id'] . '&date=' . $row['date'] . '&name=' . $row['name'] . '&score=' . $row['score'] . '&screenshot=' . $row['screenshot'] . '">Approve</a>'; } echo '</td></tr>'; } echo '</table>'; mysqli_close($dbc); ?> </body> </html>
View Code
/*** removescore.php ***/
<?php require_once('authorize.php'); ?> <!DOCTYPE html PUBLIC "-//W3C//DTD XHTML 1.0 Transitional//EN" "http://www.w3.org/TR/xhtml1/DTD/xhtml1-transitional.dtd"> <html xmlns="http://www.w3.org/1999/xhtml" xml:lang="en" lang="en"> <head> <meta http-equiv="Content-Type" content="text/html; charset=utf-8" /> <title>Guitar Wars - Remove a High Score</title> <link rel="stylesheet" type="text/css" href="style.css" /> </head> <body> <h2>Guitar Wars - Remove a High Score</h2> <?php require_once('appvars.php'); require_once('connectvars.php'); if (isset($_GET['id']) && isset($_GET['date']) && isset($_GET['name']) && isset($_GET['score']) && isset($_GET['screenshot'])) { // Grab the score data from the GET $id = $_GET['id']; $date = $_GET['date']; $name = $_GET['name']; $score = $_GET['score']; $screenshot = $_GET['screenshot']; } else if (isset($_POST['id']) && isset($_POST['name']) && isset($_POST['score'])) { // Grab the score data from the POST $id = $_POST['id']; $name = $_POST['name']; $score = $_POST['score']; } else { echo '<p class="error">Sorry, no high score was specified for removal.</p>'; } if (isset($_POST['submit'])) { if ($_POST['confirm'] == 'Yes') { // Delete the screen shot image file from the server @unlink(GW_UPLOADPATH . $screenshot); // Connect to the database $dbc = mysqli_connect(DB_HOST, DB_USER, DB_PASSWORD, DB_NAME); // Delete the score data from the database $query = "DELETE FROM guitarwars WHERE id = $id LIMIT 1"; mysqli_query($dbc, $query); mysqli_close($dbc); // Confirm success with the user echo '<p>The high score of ' . $score . ' for ' . $name . ' was successfully removed.'; } else { echo '<p class="error">The high score was not removed.</p>'; } } else if (isset($id) && isset($name) && isset($date) && isset($score)) { echo '<p>Are you sure you want to delete the following high score?</p>'; echo '<p><strong>Name: </strong>' . $name . '<br /><strong>Date: </strong>' . $date . '<br /><strong>Score: </strong>' . $score . '</p>'; echo '<form method="post" action="removescore.php">'; echo '<input type="radio" name="confirm" value="Yes" /> Yes '; echo '<input type="radio" name="confirm" value="No" checked="checked" /> No <br />'; echo '<input type="submit" value="Submit" name="submit" />'; echo '<input type="hidden" name="id" value="' . $id . '" />'; echo '<input type="hidden" name="name" value="' . $name . '" />'; echo '<input type="hidden" name="score" value="' . $score . '" />'; echo '</form>'; } echo '<p><a href="admin.php"><< Back to admin page</a></p>'; ?> </body> </html>
View Code
/*** style.css ***/
.error {
  font-weight: bold;
  color: #FF0000;
}

.topscoreheader {
  text-align: center;
  font-size: 200%;
  background-color: #36407F;
  color: #FFFFFF;
}

.score {
  font-size:150%;
  color: #36407F;
}

.scoreinfo {
  vertical-align: top;
  padding-right:15px;
}
View Code
转载于:https://www.cnblogs.com/beyond-Acm/p/4791748.html
发布者:全栈程序员-站长,转载请注明出处:https://javaforall.net/109341.html原文链接:https://javaforall.net



